

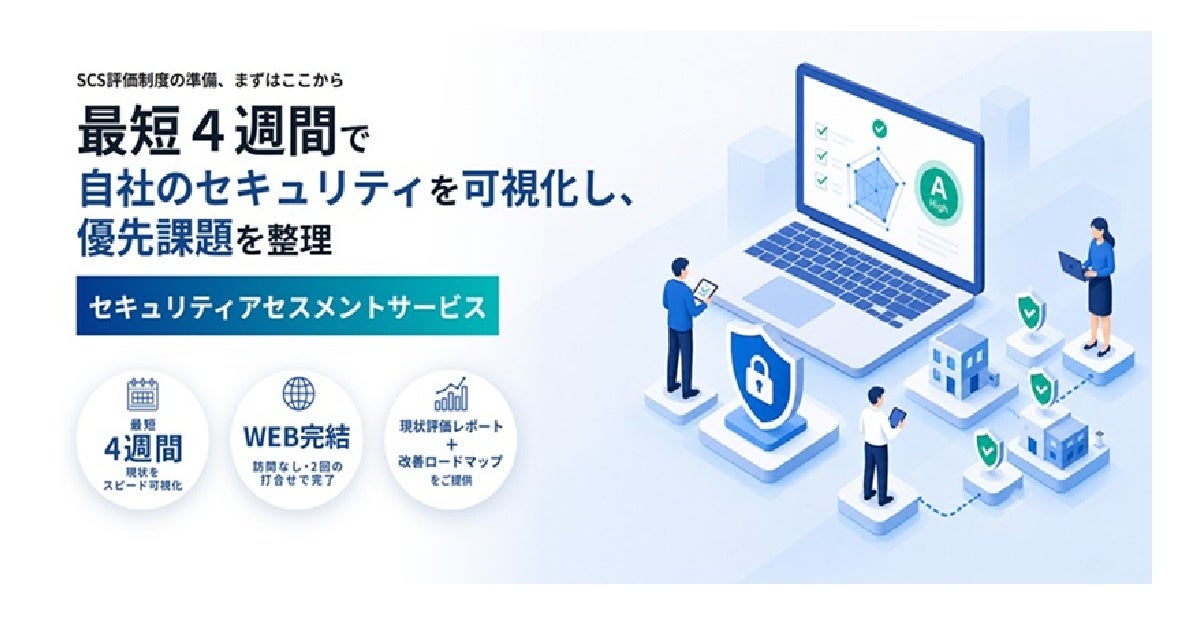
ELECOM has begun offering a new corporate "Security Assessment Service" that visualizes a company's current cybersecurity posture, starting May 27, 2026[1]. The package is designed with Japan's upcoming "Supply Chain Cybersecurity Evaluation Scheme (SCS Evaluation Scheme)" in mind. It can be completed online in as little as four weeks for a reference price of 280,000 yen excluding tax, making it accessible for mid-sized and smaller companies that often lack dedicated security staff[1].
Background: The SCS Evaluation Scheme and the Reality on the Ground
The SCS Evaluation Scheme is operated by the Information-technology Promotion Agency (IPA), under the supervision of the Ministry of Economy, Trade and Industry and the Cabinet Cybersecurity Center. It is scheduled to enter operation around the end of fiscal year 2026, and will apply broadly across industries and company sizes[1]. The aim is to lift the overall security baseline across entire supply chains.
According to ELECOM, common concerns from companies include "we cannot organize what we need to put in place," "we cannot set priorities," and "we have no security specialists in-house"[1]. The new service is positioned as a first step that helps such organizations map out their current state before tackling the scheme itself.
Online-Only, Four Weeks to "What to Do Next"
A defining feature of the package is that the entire diagnostic process is handled online, minimizing the workload for on-site staff. Meetings are limited to a kickoff hearing and a final report, with site visits and evidence reconciliation explicitly placed outside the package's scope[1]. With this design, results can be delivered in as little as four weeks[1].
If on-site verification or evidence reconciliation is required, ELECOM provides a separate quotation[1]. Conversely, companies that want to start with a desk-based review get a clear, predictable cost structure from the outset.
Seven Domains, Results Framed as "Business Risk"
The assessment covers seven core cybersecurity domains in a comprehensive manner: governance, supplier management, risk identification, protection, detection, response, and recovery. These map directly to the requirements expected by the SCS Evaluation Scheme[1].
Rather than listing technical jargon, the evaluation is delivered as "business risk" in plain language[1]. This means the output is intended not only for IT teams but also for executives, who can use it directly in investment decisions and budget discussions.
Three Deliverables, Ready for Internal Reporting and Budget Reviews
At the final report stage, ELECOM delivers three artifacts[1].
The first is a current-state summary (a checklist) based on interviews and document review. The second is a gap analysis report that quantifies the difference against the scheme's baseline. The third is a prioritized improvement roadmap[1]. All three are designed at a level of detail that companies can use directly in internal briefings and budget planning.
The service is offered under the model number GR-SCSAS01, with a reference price of 280,000 yen excluding tax and a typical delivery time of four weeks[1]. Inquiries and detailed specifications are available on ELECOM's official product page[1].
Summary
ELECOM's new Security Assessment Service offers a four-week, online-only diagnostic package aimed at Japan's SCS Evaluation Scheme, which is set to launch around the end of fiscal year 2026. With a clear price tag of 280,000 yen (excluding tax), comprehensive coverage of seven cybersecurity domains, and three deliverables aimed at executive readers, it gives even companies without dedicated security staff a practical way to start their compliance journey. In an era where supply-chain security is increasingly under scrutiny, the service expands the toolkit for organizations that want to begin with an honest look at where they stand.
[1] https://prtimes.jp/main/html/rd/p/000001418.000026881.html



























