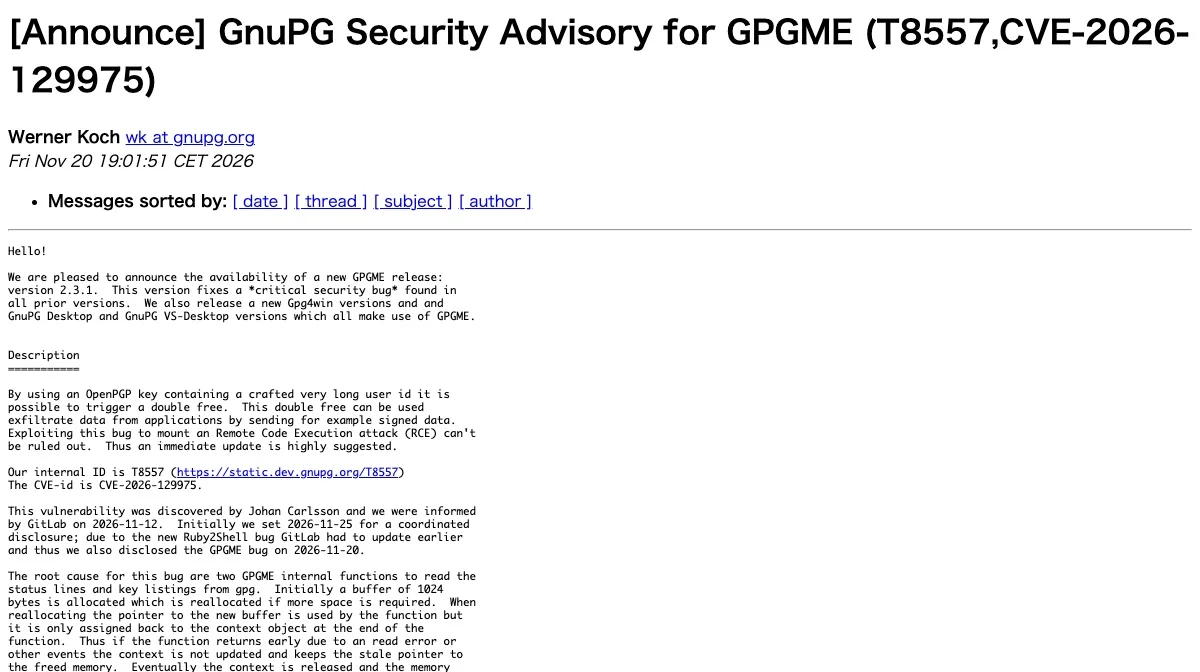
Cleverbridge, which sells software and digital products online on behalf of software companies, has disclosed that a third party copied payment card data stored on its platform. In an "Incident Update & FAQs" page on its official website, the company said it detected the unauthorized activity on November 4, 2026. It began notifying affected individuals on November 20.
Detected on November 4, systems restored the same day
According to Cleverbridge, it detected unauthorized activity on its platform on November 4 and immediately took steps to contain it. Affected systems were temporarily taken offline, and the company says all systems were back online the same day.
A subsequent investigation found that a third party had copied payment card data stored on the platform. Cleverbridge says the investigation is still ongoing as of this writing.
Asked whether this was a ransomware attack (malware that encrypts data and demands a ransom), the company answered that none of its systems were encrypted.
Which data fields and how many people were affected remain undisclosed
The official page describes the information involved as payment card details used to make a purchase through Cleverbridge. It does not specify which fields, such as card numbers, expiration dates, or security codes, were included. Cleverbridge instead tells affected individuals to refer to the notification sent to them for details.
The company has not disclosed how many people were affected or the time period of the affected purchases. The page also makes no mention of reports to law enforcement or the involvement of an outside forensic firm.
Cleverbridge sells products on behalf of software companies
Cleverbridge has offered a "Merchant of Record" (MoR) service for about 20 years, taking on sales and the legal responsibility for transactions on behalf of software companies. Its About page describes the company as a "digital reseller" that handles regional taxes, local payment methods, and regulatory requirements for its clients.
The company publishes the following figures about itself.
| Item | Figure published by Cleverbridge |
|---|---|
| Revenue processed | More than $10 billion |
| Countries and territories served | 240+ |
| Employees | 200+ |
| Offices | Chicago / Austin / London / Cologne / Singapore |
The company also says it began as a small team in Cologne, Germany.
Notifications handled with a vendor; monitoring services offered
Cleverbridge engaged TransUnion/Cyberscout as a third-party vendor to support customer notifications. The official page states that notices from this vendor are legitimate.
The company says it has offered affected cardholders credit or identity monitoring services where available. Cardholders can take up the offer by following the instructions in their notification.
Cleverbridge recommends that customers check their card statements carefully and report any unrecognized transaction to their card issuer right away, adding that the issuer may decide to replace the card. The company also warns about follow-on phishing, stating that it will never ask for card details, passwords, or security codes by email, phone, or text message.
Our Take
A merchant-of-record provider processes payments for many software companies at once. That means a single incident could reach customers who bought software without ever realizing Cleverbridge was involved. Restoring systems on the day of detection and starting notifications on November 20 is a reasonable sequence of steps.
On the other hand, the official page gives no count, no time window, and no list of the data fields involved, which makes it hard for people who have not received a notice to judge their own situation. The statement that card data was stored on the platform also leaves room for further explanation, including how that data was kept.
That said, the steps customers can take are clear. Anyone who remembers buying software or digital products from overseas vendors by card should check whether any purchase went through Cleverbridge and review their statements for suspicious charges.
Summary
Cleverbridge has disclosed that unauthorized access detected on November 4 led to a third party copying payment card data stored on its platform. The incident concerns people who bought software or digital products through the company, and affected individuals have been receiving notifications since November 20. The investigation is ongoing, and the key question now is whether Cleverbridge will provide further details on the number of people affected and the data involved.